AISTORSApplied AI and cloud engineeringBook a 30-minute call

AISTORSServicesAI governance and compliance

Service 08

AI that is safe, legal and auditable.

Written down before anyone asks for it.

For risk, legal and engineering leaders who have AI in production and nothing an assessor would accept as evidence. The gap is rarely the policy document. It is the audit trail, the model documentation, the incident playbook and the tested controls behind them. We build that evidence while the systems are being built, not reconstructed under deadline afterwards.

Book a 30-minute call
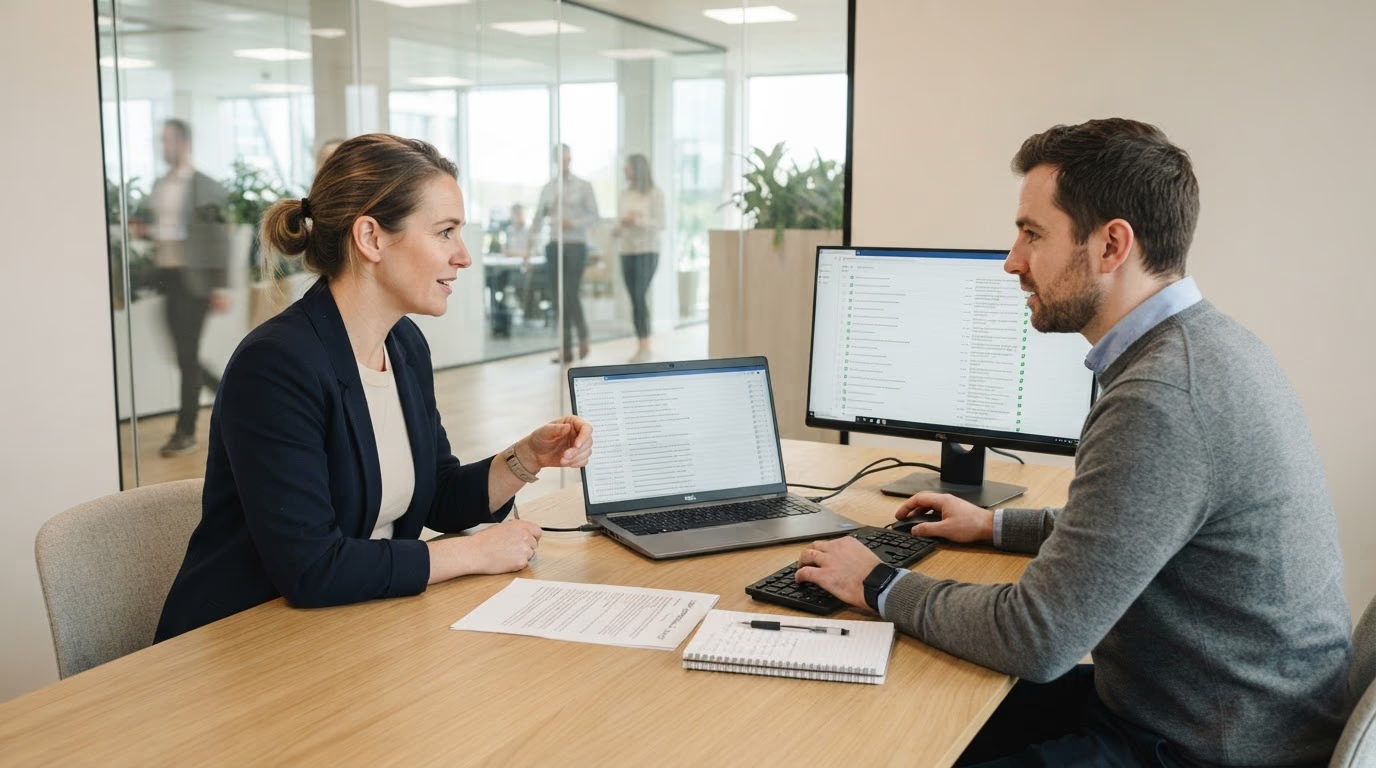
A compliance lead and an engineer at a table in a bright meeting room, a laptop showing a timestamped audit log and a monitor showing a checklist of controls with tick indicators.

What an assessor actually asks for

Not the policy document. The audit trail, the model documentation and the tested incident path behind it, built while the system is built rather than reconstructed under deadline.

01

Who this is for

If the left column is not you, say so on the call and we will tell you what would help instead.

This is for you if

  • You have AI in production already. Live systems making or shaping decisions, which is when the evidence gap stops being theoretical.
  • Somebody external will ask. A regulator, an auditor, an enterprise customer's security review or a board risk committee with a date attached.
  • You are in scope for the EU AI Act. Or you cannot yet say whether you are, which is itself the first piece of work and a cheap one.
  • You need ISO 42001 or SOC 2 readiness. And you want the technical evidence built rather than a policy pack that describes controls nobody implemented.
  • You want the failure path tested. Not just documented. What happens in the minute after an AI system is wrong, rehearsed rather than assumed.

This is not for you yet if

  • You want a certificate from us. We prepare evidence and controls; an independent assessor certifies. Anyone offering both is a conflict of interest you should decline.
  • You want legal advice. We are engineers. Whether an obligation attaches to you is a question for your counsel, and we will say so rather than guess.
  • Nothing is live and nothing is planned. Then a policy written now will describe systems you do not have. Governance is cheapest when it is built alongside the first real system.
  • You want the policy without the controls. A framework nobody implemented fails the first audit that tests it, and it is worse than nothing because it documents an intention you did not meet.
  • The deadline is next week. Evidence takes time to produce honestly. We would rather tell you what is achievable than help you present something that will not survive scrutiny.
02

What we fix, and how

Four gaps show up in almost every AI governance review. None of them is solved by a policy document.

PROBLEM 01

The policy exists and the controls do not

What we do. We implement the controls and produce the evidence that they operate: access registers, approval gates, audit logs, retention settings and the tests that show each one works. The policy then describes something real.

PROBLEM 02

Nobody can reconstruct a decision

What we do. Audit trails are designed in at build time, recording input, model version, prompt or feature set, output, and the human approval where one applied. Reconstructing this after the fact is expensive and usually incomplete.

PROBLEM 03

The model documentation is out of date

What we do. Model cards, the sub-processor list and the risk assessment are versioned alongside the system and updated from the provider's announcement rather than at audit time, so what is documented matches what is running.

PROBLEM 04

There is no tested incident path

What we do. We write the AI-specific incident playbook and then rehearse it, because an untested playbook is a document rather than a control. This is the single most commonly missing item we find.

03

What you get

Eight deliverables, all of them artefacts an assessor can read.

What we build

  • AI governance framework and policy. Written against the systems you actually run, with each control mapped to the evidence that shows it operates rather than to an intention.
  • EU AI Act readiness. Scope determination, risk classification, technical documentation and transparency obligations, worked against the current timetable and re-checked at each review.
  • ISO 42001 readiness. The AI management system, its documented controls and the evidence set, prepared for an independent assessor rather than for internal reassurance.
  • HIPAA, SOC 2, ISO 27001, GDPR and DPDP programme support. The technical and documentary evidence within our scope, with an explicit statement of what remains yours to close.
  • Audit trails and model documentation. Designed in at build time, versioned with the system, covering input, model version, output and human approval on every consequential action.
  • Security testing and red teaming. Adversarial testing of deployed systems including prompt injection, data extraction and boundary escape, with findings ranked by what they would actually let somebody do.
  • Data privacy, PII handling and residency design. What is collected, where it is processed, who can reach it and how long it is kept, designed rather than discovered during an assessment.
  • A tested AI incident playbook. Named owners, escalation path, containment steps and rollback, rehearsed at least once so it is a control and not a document.

What this is not

  • Not a compliance guarantee. No supplier can make you compliant. We produce evidence and controls; you maintain the state and an assessor certifies it.
  • Not legal advice. Whether an obligation attaches to you is a question for your counsel. We describe what the system does and where it runs.
  • Not the audit itself. We prepare, an independent assessor certifies. Doing both would be a conflict of interest and a competent auditor would flag it.
  • Not a policy pack. A framework with no implemented controls behind it fails the first audit that tests it. If you only want the document, we are the wrong supplier.
  • Not a claim to certifications we do not hold. We publish what we hold and what we do not, and we distinguish between the two on the main site.
04

How it runs

The first phase often reveals that the exposure is narrower, or wider, than assumed.

01

Scope and inventory of AI in use

Every AI system in production or planned, including the ones bought rather than built and the ones nobody registered. Shadow usage is normal and finding it is part of the work.

3 to 5 days · No production change

02

Risk classification and obligation mapping

Each system classified against the frameworks that apply to you, with the obligation and its date recorded. Where scope is genuinely uncertain, we say so rather than assume the stricter reading and inflate the work.

Obligations dated, not generalised

03

Gap assessment against the evidence set

What an assessor would ask for, what you can produce today, and what is missing. Delivered as a ranked list with effort against each item so you can decide what to close first.

You keep this whatever you decide next

04

Controls, documentation and audit trails built

Implemented in your environment, versioned with the systems they govern, and accompanied by the evidence that each control operates.

Fixed scope against the gap list

05

Red team, then rehearse the incident path

Adversarial testing of the deployed systems, findings ranked by real consequence, and one rehearsal of the incident playbook so it becomes a tested control.

Findings ranked by consequence

06

Review on the obligation calendar

Dates move, as the Digital Omnibus demonstrated. The register is re-checked against the published timetable at each review rather than trusted from the original plan.

Quarterly, or on any published change

05

Platform native

Governance evidence is produced from your own platform's native controls, not from a tool of ours.

Azure

Azure Policy and Purview for classification and lineage, Defender for Cloud posture, Entra ID access reviews, AI Foundry content safety and model logging.

AWS

Config and Control Tower for policy, CloudTrail and Audit Manager for evidence, Macie for data classification, Bedrock Guardrails and model invocation logging.

Google Cloud

Organisation Policy and Assured Workloads, Cloud Audit Logs, DLP for classification, Vertex AI model registry and safety filters.

DigitalOcean and self-hosted

Where open-weight models run in your own estate, the audit trail, access control and retention design are built explicitly, because the platform supplies less of it for you.

Everything is built on controls you already own and can keep operating after the engagement. If an assessor can only get the evidence by asking us, the control belongs to us rather than to you, which is the wrong place for it.

06

The evidence, if you want it

You do not need these numbers to recognise the problem. They are here because somebody in your approval chain will ask.

28%

of 510 senior leaders said they had incident-response playbooks for AI failures. 23 percent said they conducted adversarial testing.

Source: UST, Enterprise AI at Scale, 2026; global survey of 510 senior leaders.

86%

of organisations reported experiencing AI-related incidents.

Source: OneTrust 2026 AI-Ready Governance Report.

47%

have clear governance, oversight and controls in place, while 87 percent encourage agent use.

Source: OneTrust 2026 AI-Ready Governance Report.

The gap between the last two figures is the whole problem. Most organisations are actively encouraging agent use while fewer than half have the oversight to govern it, and incidents are already common rather than hypothetical. Set against roughly one in four having a tested incident playbook, the exposure is not that something will go wrong. It is that nobody has decided in advance what happens when it does.

07

Questions we are actually asked

Do you hold the certifications you help us achieve?

Not all of them, and we publish exactly which. We would rather tell you than have you discover it during due diligence. The current status table is in section 11 of the main site, and it distinguishes between what we help clients achieve and what we hold ourselves.

Is the EU AI Act still on the original timetable?

No, and this is the most common out-of-date assumption we meet. The Digital Omnibus on AI came into force on 27 July 2026 and moved the standalone high-risk obligations under Annex III to 2 December 2027 and the embedded high-risk obligations under Annex I to 2 August 2028. Transparency and watermarking obligations for AI-generated content apply from 2 December 2026. We re-check this timetable at every review.

We are not in the EU. Does the AI Act affect us?

Possibly, if your system is used in the EU or its output is. Territorial scope is a legal question rather than an engineering one, so we will tell you what the architecture does and where it sits, and your counsel decides whether the obligation attaches.

Can you make us compliant?

No provider can, and one that says otherwise is selling something. Compliance is a state your organisation maintains, not a deliverable we hand over. What we produce is the technical evidence, documentation and controls an assessor asks for, plus an honest list of the gaps we cannot close for you.

Do you do the audit as well?

No, and we should not. We prepare the evidence and the controls; an independent assessor certifies. A supplier who both builds the controls and signs them off is a conflict of interest you should decline.

What happens when a model provider changes something material?

It is tracked from the provider's announcement rather than discovered later. Model documentation, the sub-processor list and the risk assessment are versioned, so a change produces an update to the record instead of a silent divergence between what is documented and what is running.
08

Next step

Bring the list of AI already in use.

Thirty minutes, no obligation. Tell us what is live, who is going to ask about it, and by when. We will tell you which frameworks plausibly apply, what an assessor would ask for first, and whether the deadline is realistic.

Starts with
A fixed-scope scope-and-gap assessment. Read-only access and interviews are enough to begin.
Investment
Scoped on the introductory call, and credited in full against the remediation work that follows.
If the answer is narrower than feared
We will say so. You keep the register, the classification and the gap list. No further commitment.